As an alternative to a commercial SSL Certificate, you can also use a free Let's Encrypt certificate to implement inbound TLS Secure E-Mail in the CopiaFacts SMTP Gateway. Although you may be tempted by 'free' there are some issues to be aware of:
•There is a straightforward on-line procedure (documented at https://help.zerossl.com/hc/en-us/articles/360060119373-Creating-an-SSL-Certificate) to create a free certificate. If you use this method you will need to repeat some of this every three months, because all Let's Encrypt certificates are valid for 90 days only.
•In the initial setup, to validate and confirm your control of the domain there are two options: first to place a text file on a website at the domain, and second to put a temporary TXT record in the DNS records for the domain. Since the certificate and domain are specifically for an SMTP server, there is unlikely to be a web server running on there, so your only option will be to add a TXT record to your DNS (alongside the A and MX records already added for your server) during the first Let's Encrypt certificate-setup process.
•Instead of using the on-line method to obtain the certificate, we recommend downloading a windows command-line program instead (from the same site) to do the task. The program is run in a command session with a long command line, but the command-line only needs to be created once and the parameters are well-documented. It directly creates the necessary PFX certificate file, so involves fewer steps than the work needed to obtain a commercial certificate. It also allows the creation of a wild-card certificate covering multiple sub-domains.
•Once you have created the command-line to obtain the certificate, you add one extra parameter (for example --renew 10) to the same command to renew the certificate, as described below.
To download the command-line program, follow the link to Windows Binaries at the ZeroSSL site and download either LE32.exe or LE64.exe from https://github.com/do-know/Crypt-LE/releases. We recommend placing this program in a new folder on the machine on which the CopiaFacts SMTP Gateway is running, for example C:\SSLCERT, and using this folder for your certificate files also. The download program is all you need: it does not have an installer. You can find full, detailed instructions for running this program at https://github.com/do-know/Crypt-LE#quick-start-on-windows. The examples at that link are mostly for Linux but the parameters for LE64 are the same.
The following example demonstrates applying for a 'wild-card' Let's Encrypt certificate for *.copia.uk.com. In the examples, it is assumed that all the programs used and the files created will reside in a single working directory. If you are using a 32-bit OS, you will need to download the 32-bit versions of the programs mentioned. The dark blue items in the examples are for you to change to match your own domain.
Please read through the whole example text below before starting the procedure.
Step 1: Create an account key
You first need to create two private keys to use to obtain your certificate. This is a trivial task using the openssl utility, but unfortunately openssl is not a Windows tool. There are four ways to get around this:
•Use a Linux machine to run openssl and create the private key as described below.
•Find and install a Windows binary of openssl. There is a list of these at https://wiki.openssl.org/index.php/Binaries. We used the link to overbyte.eu, because it involves a simple install, and downloaded http://wiki.overbyte.eu/arch/openssl-1.1.0h-win64.zip. There is also a 32-bit version. Unzip the five files into a folder and run the openssl program in a command session.
•Have LE64 generate the keys for you. However it is recommended that you generate them first.
•Ask Copia to create keys for you. Copia Support will use openssl to create key files, send them to you in an encrypted ZIP, and will securely delete their copy of the keys.
The openssl command needed is:
openssl genrsa -out account.key 4096
This creates a private key which you will use to access the server in the file account.key. You can choose any name for this key.
Step 2: Create a domain key request
Using openssl as described for step 1, create a domain key. Note that the key size for this key should be different:
openssl genrsa -out copiauk.key 2048
This creates a private key which you will use for the domain in the file, for this example, copiauk.key. You can choose any name for this key.
Step 3: Create your certificate file request
This example will create a mail server certificate file with a wildcard domain name. This requires the latest version of LE64, which you will have obtained as described above.
You will require access to the control panel provided by your ISP to manage the DNS records for your domain.
Create the following command (all one line), substituting your own e-mail address and domain for the ones shown. See Step 4 for details of how to run this command:
le64 --key account.key --csr copiauk.csr --csr-key copiauk.key --crt copiauk.crt
--domains "*.copia.uk.com" --generate-missing --api 2 --handle-as dns
--email "tim@copia.com" --live --export-pfx "xzxzxzxxzxz"
Notes on the parameters of this command:.
| --key | you will normally have generated this file with openssl as described above. If you have not done so, the generate-missing clause will cause the LE64 program to generate it. |
| --csr | LE64 will generate this named file |
| --csr-key | you will normally have generated this file with openssl as described above. If you have not done so, the generate-missing clause (see below) will cause the LE64 program to generate it. |
| --crt | LE64 will generate this named file |
| --domains | This should be a comma-separated list of the domains for which the certificate is to be generated. The list must be enclosed in double-quotes. |
| --generate-missing | Required if any of the files are to be generated by LE64 |
| --api | This parameter is required, and the value must be 2, if a wild-card domain is specified. With recent versions of LE64, the default is now 2. |
| --handle-as | The value must be dns if a wild-card certificate is required. Omit this keyword and value if you are able to set up a web server on the required non-wild-card domain. |
| The value, in double-quotes, should be an admin address which will receive reminders from Let's Encrypt about renewal. Omit this keyword and parameter if you do not want this. |
| --live | Omit this parameter to generate a test certificate only. |
| --export-pfx | This required parameter causes LE64 to generate a .pfx file with the same basename the .csr file: in this example it will be copiauk.pfx. The value is the required password, in double-quotes. The .pfx file and password will be specified in GWMANAGER in order to enable TLS support in the CopiaFacts Gateway. |
| --renew | (not shown above) Add this parameter and value only when you need to renew the certificate. The value is a number of days (for example 10). A renewal certificate will only be created if the current certificate expires within the number of days specified, so the renewal command can be run at any time and it will only produce a new certificate if needed. Certificates expire after 90 days. |
Step 4: Create your certificate file
In a command session (DOS box), run the command described in step 3. After validating the parameters, the LE64 program will display the text which you must add to a TXT record in your DNS records for the domain. The procedure for doing this will depend on whether your server is administered by your corporate admin or by your ISP. Many ISPs provide users with a control panel for making DNS record changes.
For the example above, the screen would display:
Host: _acme-challenge.copia.uk.com, type: TXT, value: rCZEkUqqHvrzHXZXX3G5sRGa9evnfVBAf53IeBgZTKVkA
Wait for DNS to update by checking it with the command: nslookup -q=TXT _acme-challenge.copia.uk.com
When you see a text record returned, press <Enter>
Do not press Enter yet! First, add the TXT record with the long value string, in double-quotes. Then, in a separate command session, run the specified nslookup command until you see the TXT record displayed. Then wait at least another 15 minutes while the DNS records are propagated around the Internet. If you press Enter too soon, the validation may fail, and you will have to restart the process with a different generated value.
If the validation is successful, LE64 will proceed to create the .PFX certificate file:
2018/06/05 19:31:33 Processing the 'dns' verification for '*.copia.uk.com'
2018/06/05 19:31:33 Domain verification results for '*.copia.uk.com': success.
2018/06/05 19:31:33 You can now delete '_acme-challenge.copia.uk.com' DNS record
2018/06/05 19:31:33 Requesting domain certificate.
2018/06/05 19:31:34 Requesting issuer's certificate.
2018/06/05 19:31:34 Saving the full certificate chain to copiauk.crt.
2018/06/05 19:31:34 Exporting certificate to copiauk.pfx.
2018/06/05 19:31:34 The job is done, enjoy your certificate!
For feedback and bug reports contact us at [ https://ZeroSSL.com | https://Do-Know.com ]
Step 5: Install the Certificate in the CopiaFacts Gateway
Run GWMANAGER and enter the filename and password of the PFX file:
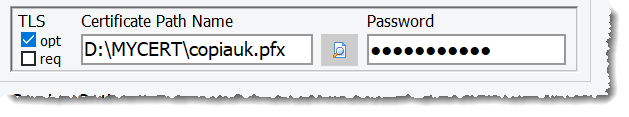
Click OK to restart the Gateway.
Step 6: Test the Certificate
To test the certificate, send an e-mail to the gateway and check that the SMTP_TLS_USED variable is set to 'yes' in the generated FS file. If you send an e-mail from your normal e-mail client, it is possible that TLS will be dropped somewhere along the path taken by the e-mail to your server, so preferably send a CopiaFacts e-mail using FFCLIENT with $email_options usetls defined on the Setup page. The SENT FS file will then also report TLS_USED as a $var_def to confirm that TLS has been used.
You can also use openssl to display the certificate used in the Gateway:
openssl s_client -connect mail.copia.uk.com:25 -starttls smtp
This command will display the contents, and details, of your certificate which will be available to a connecting mail server.
Step 7: Prepare for Renewal of the Certificate
Save the LE64 command with its parameters. You will need to re-run this with a --renew parameter before the certificate expires in 90 days time. You will see a warning message in GWMANAGER when the renewal date is imminent:
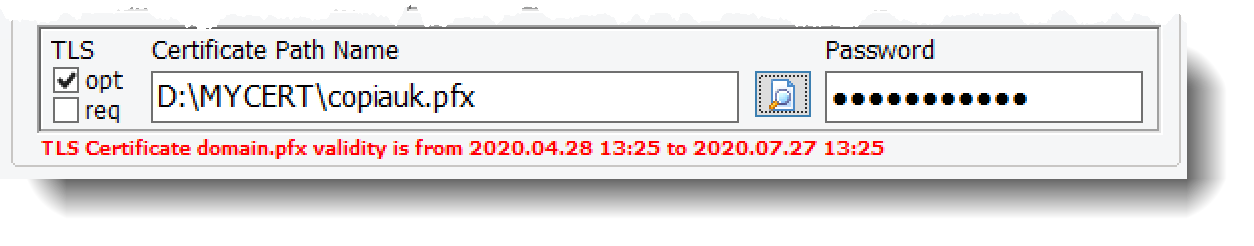
Provided you renew your certificate well before expiration, Let's Encrypt will not require a re-authorization of your DNS records. However Let's Encrypt policy in this area changes from time to time and re-authorization may be requested.